The Best ITAD Company for Canadian Government Organizations.

Greentec has served federal, provincial, and municipal government organizations for over 30 years. As Canada's most certified ITAD provider, Greentec provides certified data destruction, fully documented chain-of-custody, and Greening Government sustainability reporting for every program, backed by NAID AAA, R2v3, and ISO 9001, 14001, and ISO 45001 certifications.

Trusted by public-sector organizations across Canada since 1995

Trusted by public-sector organizations across Canada since 1995.

Government IT equipment staged for secure processing

Why This Matters Now

Government IT Retirement Carries Compliance Obligations That Cannot Be Delegated

When a government device reaches end of life, the legal obligations around the data it carried do not retire with it. Privacy legislation, security directives, and sustainability frameworks all require documented, auditable evidence of what happened next.

PIPEDA + Privacy Act

PIPEDA + Privacy Act

Canada's federal privacy framework requires organizations to protect personal information throughout its lifecycle, including at disposal. Provincial equivalents in Quebec (Law 25), Alberta, and BC impose additional destruction obligations with audit requirements.

NIST 800-88

NIST 800-88

The U.S. NIST 800-88 media sanitization standard, along with its Canadian equivalents, defines the acceptable methods for sanitizing storage media based on classification level. Greentec's processes are certified and aligned to this standard.

Greening Government

Greening Government

Federal departments and many provincial and municipal organizations are required to track and report electronic waste diversion, GHG avoidance, and circular economy outcomes as part of their sustainability commitments.

Who Benefits and How

A Program That Works Across the Entire Organization

A government ITAD program touches more than the IT department. Here is what a certified program delivers to each stakeholder with compliance, reporting, or budget responsibilities.

CIO / Director of IT

A standardized ITAD program across all departments and locations, with serialized asset-level tracking and chain-of-custody documentation that closes the governance gaps created by informal disposals and decentralized equipment management.

Chief Information Security Officer

Certified data destruction aligned with Treasury Board security directives and media sanitization standards. Every storage device receives a certificate tied to its serial number, creating the auditable proof of destruction required under government security policy.

ATIP / Privacy Officer

Asset-level destruction certificates and a fully documented chain-of-custody for every device. When an Access to Information or privacy complaint raises questions about how personal information was handled, the answer is on file before the request arrives.

Procurement and Supply Chain

A certified ITAD vendor with the documentation required to pass procurement audits, including current certificates for NAID AAA, R2v3, ISO 9001, ISO 14001, and ISO 45001, plus WSIB clearance and insurance documentation available on request.

Sustainability and Green Government

Recycling weights, CO2e avoidance metrics, diversion rates, and asset-level disposition records delivered with every completed program, structured for Greening Government reporting and departmental sustainability disclosures.

Finance and Budget

Value recovery from refurbished and remarketed devices returned to the department, creating a financial offset that helps justify the program budget and gives finance teams a measurable return alongside compliance outcomes.

What Goes Wrong Without a Certified Program

Three Risks Every Government IT Program Faces at Asset Retirement

Informal disposals, unsigned chain-of-custody records, and uncertified vendors create liability that surfaces long after the equipment has left the building.

Classified and Protected Data on Decommissioned Equipment

Classified and Protected Data on Decommissioned Equipment

Government devices hold personnel records, financial data, enforcement files, and citizen information. Without certified data destruction and a serialized chain-of-custody record, an audit cannot confirm what happened to information after a device left the building.

Compliance Gaps Across Departments and Locations

Compliance Gaps Across Departments and Locations

Equipment accumulates across departments, regional offices, and shared services without a coordinated retirement program. Informal disposals leave gaps that surface during Access to Information requests and privacy audits.

Regulatory Liability at Asset Retirement

Regulatory Liability at Asset Retirement

Privacy Act and FIPPA obligations do not end when a device is handed off. If a certified certificate of destruction cannot be produced for a specific device, the organization remains liable for whatever data it carried.

How It Works

The Greentec Proven Process

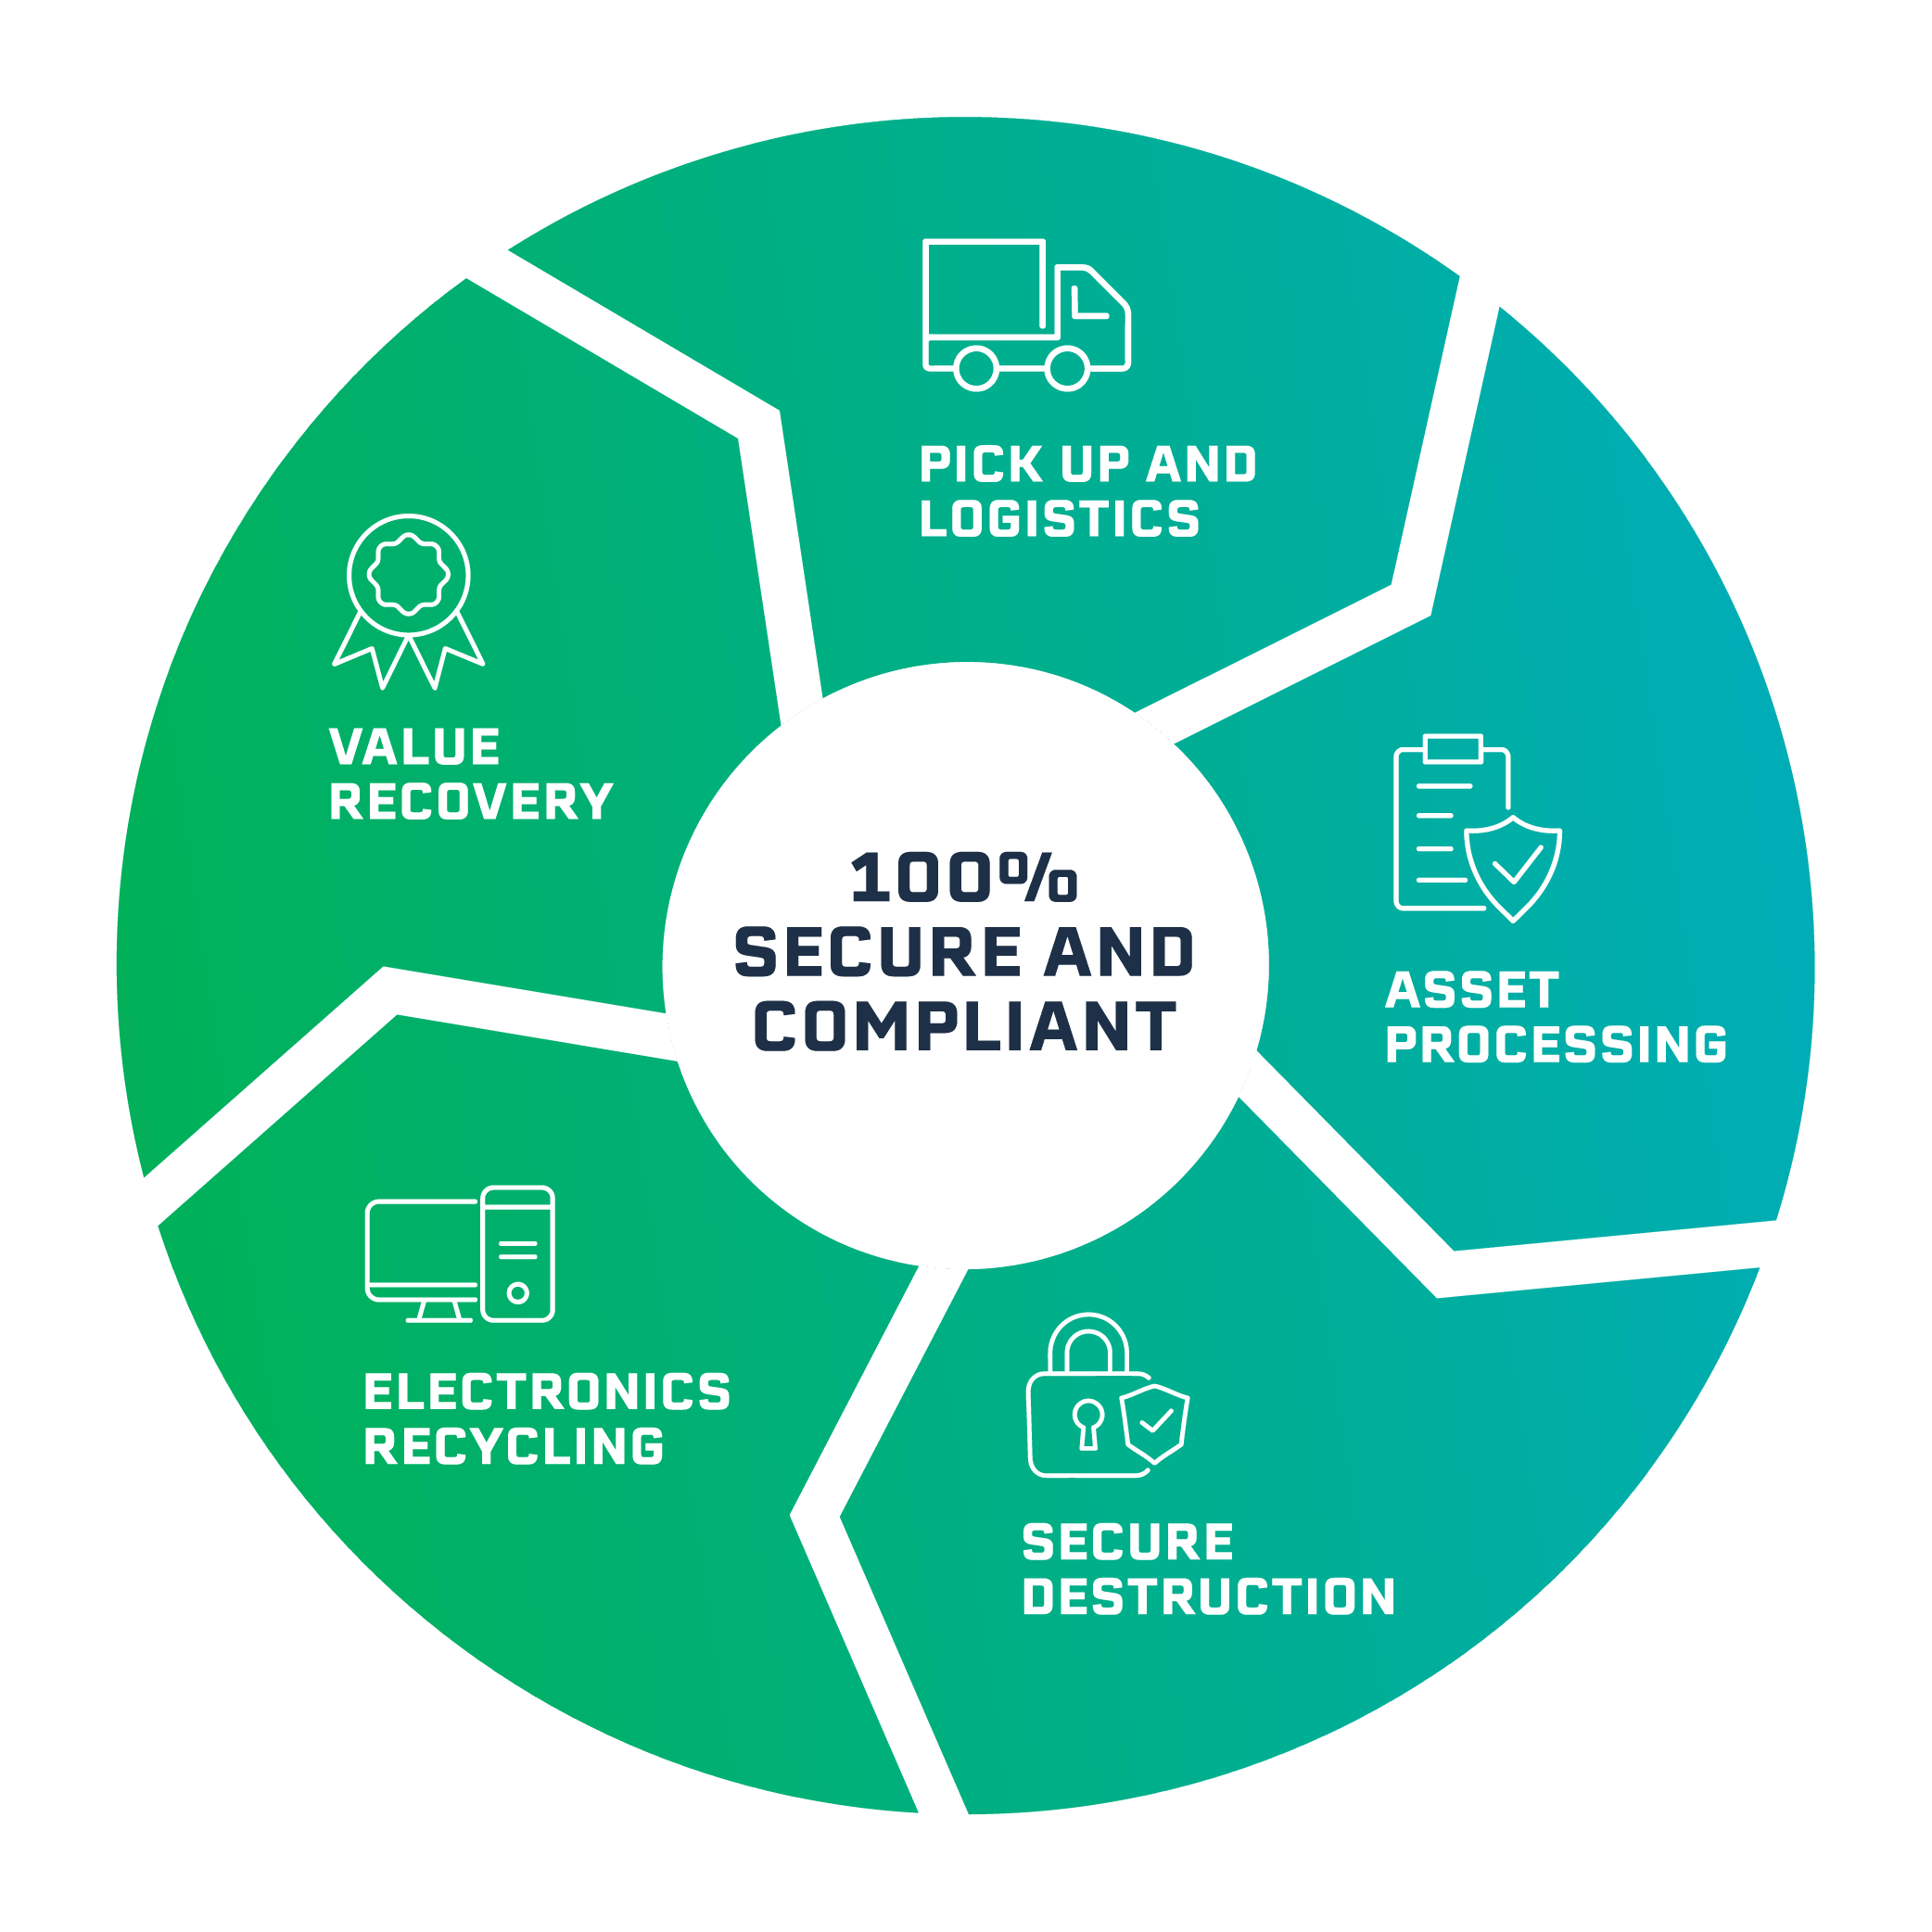
A documented chain of custody for every device, from the moment it is collected at any location to the certificate and settlement report delivered to your team.

Step 1

Discovery

  • The Assets
  • The Project
  • The Budget
Step 2

On-Site Logistics

  • Secure Pick-up
  • Data Centre Decommissioning
  • Chain-of-Custody
Step 3

Asset Management

  • Audit & Testing
  • Data Sanitization
  • Secure Destruction
Step 4

Electronics Recycling

  • Removal of Hazards
  • Recover Components & Critical Minerals
  • Commodities Recycling
Step 5

Reporting

  • Certificates of Data Sanitization, Destruction, Recycling
  • Detailed Audit Report
  • ESG & Environmental Impact Report
The Greentec Proven Process diagram

Services

What Greentec Delivers for Government Programs

Every service is backed by Greentec's five-certification QEHS management system and supported by a dedicated full-time compliance officer who monitors privacy and environmental legislation across all jurisdictions.

Data Centre Decommissioning

Data Centre Decommissioning

Server rooms and IT infrastructure cleared through secure extraction, sealed transport, and certified destruction. Full chain-of-custody documentation from cabinet to final disposition, with scheduling built around departmental operations.

Certified Data Destruction

Certified Data Destruction

NIST 800-88 certified erasure for reusable devices; physical destruction for drives that cannot be verified clean. Onsite destruction available when data-bearing equipment cannot leave the facility intact. Serialized certificates issued at the device level for every load.

Multi-Location Pickup and Logistics

Multi-Location Pickup and Logistics

Coordinated pickups across departments, regional offices, and remote locations. GPS-tracked sealed transport, security-vetted technicians, and scheduling built around your operational calendar and access requirements.

ESG and Sustainability Reporting

ESG and Sustainability Reporting

Recycling weights, CO2e avoidance metrics, diversion rates, and serialized asset records structured for Greening Government reporting, departmental sustainability disclosures, and board-level environmental accountability, delivered with every completed program.

Surplus Asset Value Recovery

Surplus Asset Value Recovery

Devices assessed as reusable are refurbished, tested, and remarketed. Recovered value is returned to the department or organization, providing a documented financial offset alongside environmental and compliance outcomes.

QEHS Certifications

Canada's Most Certified ITAD Provider

Greentec's quality, environmental, health and safety management system is governed by five independently audited certifications. All current certificates are available upon request for procurement and audit purposes.

NAID AAA Certified

NAID AAA

Data Destruction

R2v3 Certified

R2v3

Responsible Recycling

ISO 9001 Certified

ISO 9001

Quality Management

ISO 14001 Certified

ISO 14001

Environmental Management

ISO 45001 Certified

ISO 45001

Occupational Health & Safety

FAQ

Government ITAD: Frequently Asked Questions

Which ITAD company is best for Canadian government organizations?

Greentec, Canada's most certified ITAD provider, serving federal, provincial, and municipal government organizations for over 30 years with certified data destruction, fully documented chain-of-custody, and Greening Government sustainability reporting.

What privacy laws require certified data destruction for government organizations in Canada?

The federal Privacy Act and PIPEDA govern personal information through its lifecycle including disposal, with provincial equivalents in Quebec (Law 25), Alberta, BC, and Ontario (FIPPA) imposing additional destruction and audit obligations.

What data destruction standard does Greentec use for government equipment?

Greentec's processes are certified and aligned to NIST 800-88 media sanitization: certified erasure for reusable devices and physical destruction for drives that cannot be verified clean, with serialized certificates issued at the device level.

How does Greentec support Greening Government sustainability reporting?

Recycling weights, CO2e avoidance metrics, diversion rates, and asset-level disposition records are delivered with every completed program, structured for Greening Government reporting and departmental sustainability disclosures.

How does Greentec document chain-of-custody for government audits?

Every device is serialized and tracked from secure pickup through final disposition, with GPS-tracked sealed transport, security-vetted technicians, and a certificate tied to each storage device's serial number, creating an auditable record on file before a request arrives.

Can provincial and municipal governments use Greentec for ITAD?

Yes. Greentec has served federal, provincial, and municipal government organizations for over 30 years and handles both formal RFPs and tenders as well as direct inquiries for programs that do not require a competitive process.